Published to clients: March 10, 2026 ID: TBW2074
Published to Whisper Club: March 10, 2026
Analyst(s): Dr. Doreen Galli
Photojournalist(s): Dr. Doreen Galli
Abstract:
“This Whisper Report address the question regarding the best practices for integrating AI and ML into our security Systems. It highlights how leaders emphasize protecting PII, using selective data movement, optimizing hardware, choosing the right models, and knowing when AI should not be applied. Insights come from LVT’s Steve Lindsey, Safr’s John Cassise, 360 Privacy’s Trinity Davis, Intel’s Mike Nielsen, RightCrowd’s Jason Bohrer, Bioconnect’s Edsel Shreve, Vaidio’s Marshall Tyler, and Databuoy’s Kathleen Griggs. “
Target Audience Titles:
- Chief Technology Officer, Chief Security Officer, Chief Information and Security Officer, Chief Trust Officer, Chief Compliance Officer, Chief Risk Officer
- Head of Product, VP of Product, Chief Marking Officer, Data Protection Officer,
- Enterprise Architect, Director of Data Protection, Director of Data Governance, Chief Privacy Officer
Key Takeaways
- Protect PII rigorously, as regulations vary widely and AI accelerates exposure risks.
- Use selective data movement and confidential computing to minimize PII transfer and strengthen security.
- Apply the three‑way test: AI must improve speed, accuracy, or cost efficiency to justify deployment.
- Choose NDAA‑compliant, learning‑capable hardware to ensure secure and adaptive edge performance.
What are the best practices for integrating AI and machine learning into our security systems?
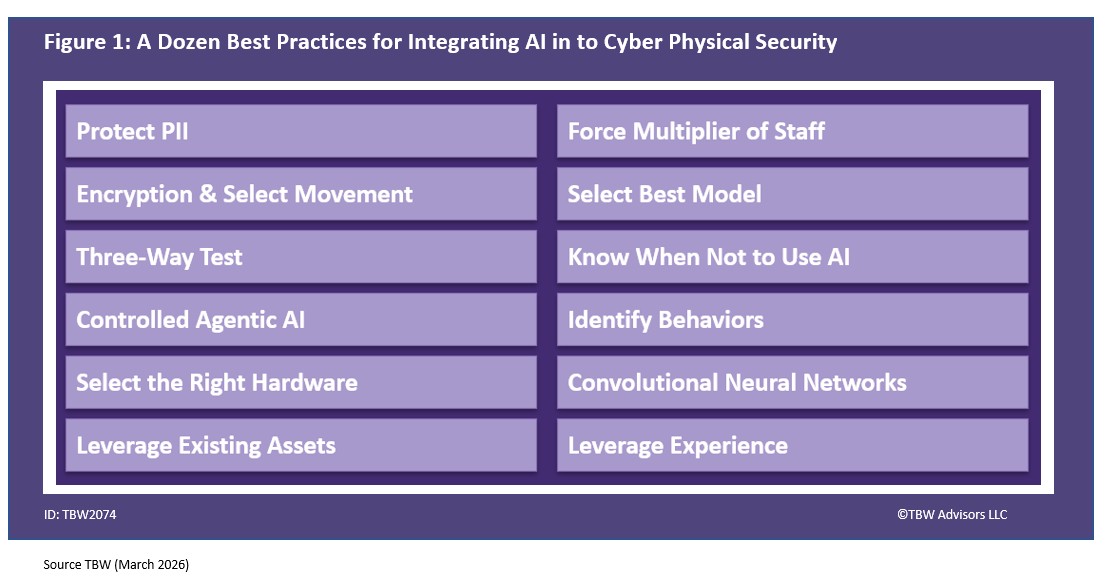
We took the most frequently asked and most urgent technology questions straight to the cyber physical security experts gathering at ISC West 2025. This Whisper Report addresses the question regarding what are the best practices for integrating AI and machine learning into our security systems as depicted in Figure 1. Just in case anyone is not sure that AI has a place in security, LVT’s Steve Lindsey said it best, “physical security and the problems and threats we’re dealing with are just increasing and increasing the problem is our budgets to deal with those are staying the same so the mathematical equation says that we have to do more with less.” It’s a matter of simple math. Since we are dealing with the cyber physical world at ISC West, we will start with cautions specifically regarding PII information (personally identifiable information) and then highlight best practice recommendations.
1. Protect PII
When it comes to the cyber physical security world and AI, one must keep in mind that some data is PII data. One cannot do anything with AI unless the PII data is protected. As Safr’s John Cassise called out, “we are talking about PII so that means that we’re dealing with people’s personal information and this is a situation that that changes from state to state sometimes even county to county so you need to have a platform that is flexible enough to accommodate.” At the same time, keep in mind as 360 Privacy’s Trinity Davis cautions, “we’re super concerned about AI. AI is actually bit driven by Big Data we’re actually seeing a lot of these language models actually turn up they expedite the process in which somebody can identify your PII.” Thus, the environment for PII is dynamic that varies by location while at the same time is increasingly under attack due to AI.
2. Encryption and Select Movement
Safr’s John Cassise was quick to point out that it is about, “how we transmit data? Is it secured? Is it secure at rest in transit but also do I have the flexibility to decide that this particular piece of information isn’t necessary so I don’t need to move that around my system?” To that we would like to remind clients and subscribers, it is possible to do better than only encryption at rest and in transit. Specifically, it is possible to also be secure while computing leveraging confidential computing available in most public clouds. For additional research on confidential computing see, Industry Whispers: Public is Private – Confidential Computing in the Cloud | TBW ADVISORS.
In terms of selecting what data to move, Cassise goes on to further explain, “for instance the human readable face I don’t necessarily need to move for my system to operate so do I choose an a variation that allows me to not move that around but just the biometric signature.” This approach is also supported by Intel RealSense’s Mike Nielsen. “Authentication without distributing PII.. about 512 bytes that’s irreversible back to a human image now I would then go back to that camera it would evaluate me again generate a new template and then we compare those templates so we’re not comparing my face we’re comparing a template generated as 80 points and the relational distances of those points on my face.” While this is part of the standard, we heard about it often during our coverage for Conference Whispers: ISC West 2025 but did not hear about it during our coverage for Conference Whispers: Identiverse 2025. That said, once I inquired if the PII information was transferred to the badge or a hash – all confirmed the solutions kept to the standard.
3. Three-Way Test
LVT’s Steve Lindsey got right to the point in terms of how he recommends selecting AI projects. “It has to make things faster, more accurate, and lower cost and if technology isn’t solving one of those three questions, then it’s really not useful to us.” Now those are three business problems most organizations can appreciate. As we have repeatedly advised, AI project must solve business problems – it is not just about using ‘AI’. If you are unsure if your project is a great candidate to solve with current technology, be sure to schedule your inquiry so a TBW Advisors expert can advise you appropriately.
4. Controlled Agentic AI
RightCrowd’s Jason Bohrer recommends the ever-growing area of Agentic AI with a bit of caution. “There’s a lot of unique opportunities around how you best adopt some of the agent capabilities associated with AI right. It all has to be controlled and approved through the proper channels to make sure you’re driving efficiency, but it also has the proper approval processes associated with it too and we also have Incorporated that some of that into our platform as well.” Before one can dive into Agentic AI, one’s processes must be optimized and data cleaned. If this challenge is your Mt. Everest, be sure to schedule your inquiries with your analyst. At TBW Advisors we offer a lot of firsthand experience and expertise in process optimization and the creation and optimization of advanced data mesh.
5. Select the Right Hardware
If your hardware can compromise your solution, this is a problem anywhere in IT. In the cyber physical world where the hardware can be located out on remote edges, hardware selection becomes even more critical. As Safr’s John Cassise stated, “number one we need to make sure that we’re using chipsets that are NDAA compliant right because we’re talking about privacy and we can’t be using chips from Chinese manufacturers that potentially are giving vulnerabilities.” But the hardware can do more than just stay compliant and secure. As Bioconnect’s Edsel Shreve declared, “these devices .. are learning devices they have an NPU chip whether you call it API AI or machine learning one of the things these devices do is every single time you use them they’re actually improving the template they’re learning and so over time you just get a stronger and stronger template.”
6. Leverage Existing Assets
The best practice in any organization is to leverage existing organizational assets. For example, as Bioconnect’s Edsel Shreve explains, “We see AI tools and machine learning coming into place is taking all of the telemetry and data from these systems right just in terms of just this performance of the system or any issues about how they react on a network if servers or readers are dropping offline.” Leveraging existing organizational data particularly telemetry data, is a great practice for any organization. It is important to ensure the data has quality before looking for patterns or making decisions based on the data.
7. Force Multiplier of Staff
One great practice when deploying AI within your organization particularly in the space of cyber physical security is ensuring the ROI. Specifically, as LVT’s Steve Lindsey pointed out, “what AI is helping us to be able to do is to start being a force multiplier for our people. And it doesn’t limit itself to just computer vision models being able to detect things. There has to be intelligence that consumes those detections and now can intelligently make a decision on what should I do with this. As intelligence gets smarter it can actually help deter and do things for us before humans get
involved in fact at LVT we find that up to 90% of the time an effective deterrence that is believable will get the person to go away which means that five 5 to 10% of the time we’re dealing with somebody who’s desperate or not lucid and they’re going to do it anyway.” Only bothering human security agents in 10% of the incidents when they are needed? That will enable staff to do more with less.
8. Select Best Model
Selecting the best model for your use case sounds like an obvious best practice but it is more nuanced than one might think. As Viadio’s Marshall Tyler articulated, “technology takes different resources and there are a lot of different models out there you want tried and true model optimization based on your needs for how accurate how quickly and how cost effectively you want to be able to respond to different types of incidents. Technology takes different resources and there are a lot of different models out there. You want tried and true model optimization based on your needs for how accurate how quickly and how cost effectively you want to be able to respond to different types of incidents.” Its about accommodating the entire solution needs and how a given model fits into the solution requirements.
9. Know When not to Use AI
Kathleen Griggs from Databuoy shared a brilliant best practice regarding the use of AI for security. “When it comes to a life safety situation, we’ve designed our system to get it right. To filter it out based on physics and what we know about the signal and that’s where we feel like it’s not the best place to put AI really.” In other words, when the exact precise math of physics can give you an exact answer, why use AI to approximate. This is particularly true in life and death scenarios.
10. Identify Behaviors
We often advise, it is never about if a specific model meets your needs. AI models will fail. It is about bringing together a collection of models to achieve the solution. It is always about the soluton succeeding. One valuable model to add into a solution is one that can identify behaviors. As Intel’s Mike Nielsen reportedv, “we’re seeing the industry do now is using some of the same techniques to
identify behaviors and objects and “ in the context of physical security to identify bad stuff that could be happening is it actually a gun that’s that there’s a high fidelity way to determine a weapon by looking at a weapon against a database of weapons behaviors like am I reaching for a gun that’s a much lower fidelity thing to do but it still allows Security Professionals to act and respond if a machine detects that somebody may be taking something out of a pocket that they should be doing so those same techniques that we apply to facial Biometrics we are seeing the same techniques being applied in the industry to detect objects detect behaviors and then detect emotions pull those three together and evaluate what action should be taken as a result.”
11. Convolutional Neural Networks or CNNs
A true best practice for layering together various models or algorithms is one commonly referred to as CNNs. As Intel’s Mike Nielsen highlighted, “we apply convolutional neural networks which is a classic but Advanced technique of evaluating an image through layers partitioning that to multiple algorithms to determine things like is it a human being face is that face an actual person is it a mask are they wearing glasses are they wearing a hat are they wearing a Covid mask and we use multiple layering technique with CNNs that allows the machine to learn exactly what is on the face is it an actual face and then applying additional techniques to determine whose face it belongs to.”
12. Leverage Experience
Last but definitely not least, Vaidio’s Marshall Tyler gave some really sound advice for a must follow best practice. “It’s really important you’re looking at one the pedigree of the company that’s been doing the AI. Is this something they just started are they trying to use fancy new Technologies? Make sure that you’re thinking about how fast you can get answers, how accurate those answers are, how efficiently and cost effectively you can drive those answers.” TBW Advisors LLC has witnessed countless examples of AI projects that wasted millions and months because they didn’t work with someone with extensive true experience. Reduce your risk and increase your success by scheduling your inquiry with your TBW Advisors expert to get the best advise available before charging ahead.
Related playlists
- Industry Whispers: Public is Private – Confidential Computing in the Cloud | TBW ADVISORS
- Conference Whispers: Black Hat USA 2019
- Whisper Report: How can we enhance our cybersecurity measures to protect against emerging Cyber Physical threats?
- Conference Whispers: ISC West 2025
- Conference Whispers: Identiverse 2025
- Playlist for Whisper Report: What are the best practices for integrating AI and machine learning into our security systems?
Corporate Headquarters
2884 Grand Helios Way
Henderson, NV 89052
Downloading, re-uploading, or redistributing this file is not permitted under any license.
©2019-2026 TBW Advisors LLC. All rights reserved. TBW, Technical Business Whispers, Fact-based research and Advisory, Conference Whispers, Industry Whispers, Email Whispers, The Answer is always in the Whispers, Whisper Reports, Whisper Studies, Whisper Ranking, Whisper Club, and One Change a Month, Vegas Convention Library; Leading Professionals, Real Questions, Real Time, are trademarks or registered trademarks of TBW Advisors LLC. This publication may not be reproduced or distributed in any form without TBW’s prior written permission. It consists of the opinions of TBW’s research organization which should not be construed as statements of fact. While the information contained in this publication has been obtained from sources believed to be reliable, TBW disclaims all warranties as to the accuracy, completeness or adequacy of such information. TBW does not provide legal or investment advice and its research should not be construed or used as such. Your access and use of this publication are governed by the TBW Usage Policy. TBW research is produced independently by its research organization without influence or input from a third party. For further information, see Fact-based research publications on our website for more details.