Published Whisper Club: July 27, 2026 ID: TBW2092
Public: October 12, 2026
Analyst(s): Dr. Doreen Galli
Photojournalist(s): Dr. Doreen Galli
ABSTRACT
“This Whisper Report investigates what the next SolarWinds-level breach waiting to happen may be. Filmed at Black Hat USA 2025 in Las Vegas, it examines how rapidly evolving technologies are introducing new risks that organizations may not yet fully understand. Experts explore where these emerging vulnerabilities could surface at scale. Cited experts: Jonathan Rende Checkmarx, James Spiteri Elastic Security, Alex Lanstein StrikeReady, Brian Mehlman Cyber Innovate, Thomas Roccia Microsoft, Ariful Huq Exaforce, David DellaPelle Dune Security, Saket Bajoria Safe Security.”
Target Audience Titles:
- Chief Information Security Officer, Chief Technology Officer, Chief Digital Officer, Chief Information Officer
- Chief Product Officer, Chief Experience Officer
- IAM engineers, Security Architects, DevSecOps Engineers, IT Ops Managers, Application Security Architects, AI security specialists, Cyber Risk analysis
Key Takeaways
- AI protocols are being deployed faster than they’re secured.
- Cloud and AI supply chains are high-risk blind spots.
- Poorly trained AI systems can reflect dangerous human biases.
- Autonomous agents may soon breach systems independently.
- Developer practices like vibe coding introduce new vulnerabilities.
- Attackers are exploiting encrypted communication platforms.
- Resilience—not just prevention—is essential for breach readiness.
What’s the next SolarWinds-level breach waiting to happen?
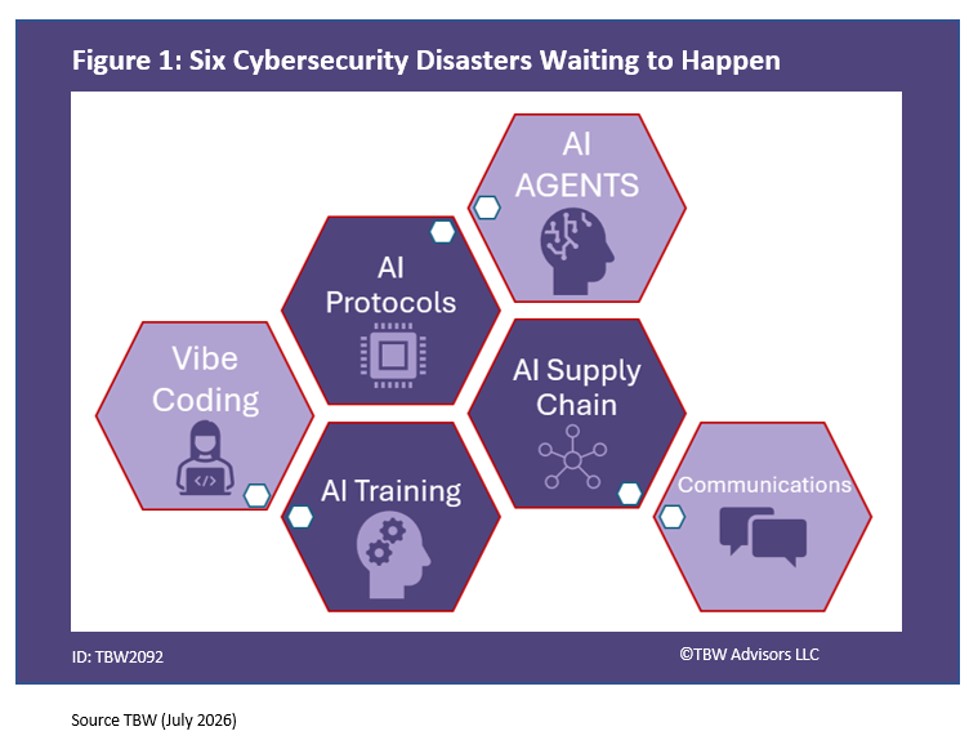
We took the most frequently asked and most urgent technology questions straight to the Cybersecurity professionals gathering at Black Hat USA 2025 held in Las Vegas. This Whisper Report addresses the question regarding what’s the next SolarWinds-level breach waiting to happen? Figure 1 contains an image representing the seven possible cybersecurity disasters on the scale of SolarWinds waiting to happen.
1. AI Protocols: Innovation Without Guardrails
Our first area of concern comes to us from Checkmarx’s Jonathan Rende, “It will be something related to AI.” Elastic Security’s James Spiteri further expanded. “ the next big attack is going to be against some of these new AI protocols that we’re seeing. Uh they’re being adopted really quickly without actually taking a step back to understand what we’re actually implementing. So things like the model context protocol, which is amazing at what it allows people to do, but if you don’t do it right, if you don’t implement it right, that can have catastrophic results. like it doesn’t do verification today. The authentication mechanisms are not to where it needs to be yet. But we’re still seeing really wide deployments of it. And that is a really uh easy attack vector for something like uh another big attack to happen.” AI Protocols penetrating systems and getting penetration before their identity and access control mechanisms are fully mature – that does sound concerning.
2. AI Supply Chain & Cloud Infrastructure Risks
The more foundational a technology, the more disruptive it becomes if it is breached. StrikeReady’s Alex Lanstein has his eye on the public clouds. “a breach of a major cloud provider. It could be a cloud software provider, could be a cloud hardware provider. But if I were to look at what is the most difficult for enterprises to detect, which part of what made Solar Wind so effective and made Fire Eye the only company to detect it, even though it affected over 10,000 organizations, I think a breach of your cloud provider where you don’t have instrumentation and logging and visibility and they might not play as nice with you as as you would like. I think that is the next Solar Winds bridge.” Cyber Innovate’s Brain Mehlman and his AI Agent Ralph ultimately agreed. “So the next big breach might not be a traditional software vulnerability. It could be a compromise in the AI supply chain or a cloud service that everyone trusts. So that’s what I’d keep an eye on.”
3. Human Oversight in AI Training
Our third potential risk also comes from Cyber Innovate’s Brian Mehlman and AI Agent Ralph. Once again, AI is on their mind. “one of the biggest risks is when you have these systems being trained or shaped without any human guidance or oversight. If someone who maybe isn’t fully equipped to handle that responsibility is the one doing the training, you can get systems that pick up on really problematic behaviors. They might learn biases. They might learn unstable patterns. And basically you end up with an AI that’s reflecting the cognitive quirks or even the struggles of the person who trained it. And you’re right, that’s a big deal.” AI is trained by humans. It can become the best of humanity or reflect the worse of humanity.
4. Emerging Threats from Autonomous Agents
One scenario that many are afraid to speak about comes to us from Microsoft’s Thomas Roccia. “Future attack will be powered by AI system and agent and potentially an agent will be able to breach a system autonomously and give back the information to the attacker. That’s something that could be possible. There is already some work around that and some attackers are taking advantage of this technology. So we are still waiting to see what uh what the future will be.” Nothing like getting autonomously breached.
5. Developer Practices & Vibe Coding
A lot of organizations have moved to leveraging AI to assist with writing their actual code for the product. Exaforce’s Ariful Huq extends some caution. “Vibe coding is going to be an important area for every enterprise to start looking at because what’s happening is you have developers essentially leveraging this type of coding using cloud and cursor and all these technologies that are out there. This code really needs to be vetted before it’s deployed in production because it could potentially have many attack vectors related to supply chain or potentially uh you know the way the code is written potentially getting exploited. So I think this is one of the most important threat vectors because you have thousands of developers actually probably more than thousands leveraging this kind of technology and it is sort of like uncharted territory right now.” Of course, we do depend on the human in the loop; however, the newest generation of coders may have never written code without AI’s help perhaps increasing the vulnerability.
6. Communication Channels as Attack Vectors
One final possible area of concern, this time NOT dealing with AI involves our communication channels. Dune Security’s David DellaPelle extends this caution. “there’s a massive blind spot in today’s organizations and businesses. What’s happening now is attackers and APT groups (Advanced Persistent Threat) like Scattered Spider are not just going through email, right, to socially engineer users. They’re not just going through SMS and delivering, you know, smishing. They’re even going into personal and encrypted communication channels, things like Signal and WhatsApp and Telegram. These are highly effective and collaborative solutions for people to communicate with each other across borders instantaneously and encrypted fashions. But unfortunately the attackers are now using those types of of channels at scale using AI to you know again the quantity and the quality of attacks using these types of channels to solicit users to extort users or to just manipulate and socially engineer users in in other ways.” Any and every channel being leveraging for corporate communications and corporate information exchange must be protected.
Takeaway advice: Resilience Over Prevention
While we may not know when or how an attack will occur, there is still something organizations can do. As Safe Security’s Saket Bajoria reminded us all, “it’s a matter of when not if, right? So it it is going to happen no matter what you do. Right now the only way to defend that is resiliency. If you have built resiliency of recovering fast, if you have thought about you know I’m ready for a ransomware, I’m ready for a data excfiltration. I’m ready for a DOS. I’m ready for system outage. When you’re already ready for these big events, you already you can reduce your recovery time. Some people who are just in denial.” Something that cannot be emphasized enough, do what you can to prevent but also make sure you organization is prepared for WHEN it occurs.
Related playlists and Publications
- Whisper Report: How can organizations implement zero-trust security without disrupting user experience?
- Conference Whispers: Identiverse 2025
- Conference Whispers: Identiverse
Corporate Headquarters
2884 Grand Helios Way
Henderson, NV 89052
Downloading, re-uploading, or redistributing this file is not permitted under any license.
©2019-2026 TBW Advisors LLC. All rights reserved. TBW, Technical Business Whispers, Fact-based research and Advisory, Conference Whispers, Industry Whispers, Email Whispers, The Answer is always in the Whispers, Whisper Reports, Whisper Studies, Whisper Ranking, Whisper Club, and One Change a Month, Vegas Convention Library; Leading Professionals, Real Questions, Real Time, are trademarks or registered trademarks of TBW Advisors LLC. This publication may not be reproduced or distributed in any form without TBW’s prior written permission. It consists of the opinions of TBW’s research organization which should not be construed as statements of fact. While the information contained in this publication has been obtained from sources believed to be reliable, TBW disclaims all warranties as to the accuracy, completeness or adequacy of such information. TBW does not provide legal or investment advice and its research should not be construed or used as such. Your access and use of this publication are governed by the TBW Usage Policy. TBW research is produced independently by its research organization without influence or input from a third party. For further information, see Fact-based research publications on our website for more details.